SaaS and Custom Software
Cyber Security
Security Reviewed at Every Stage, Not Just Before Launch
We build security review into the architecture stage, not as a scramble the week before launch. Access controls, data handling and dependency checks are part of how we work throughout - with a dedicated penetration test and audit available for higher-risk projects that need one.
9
real SaaS and Custom Software projects
★
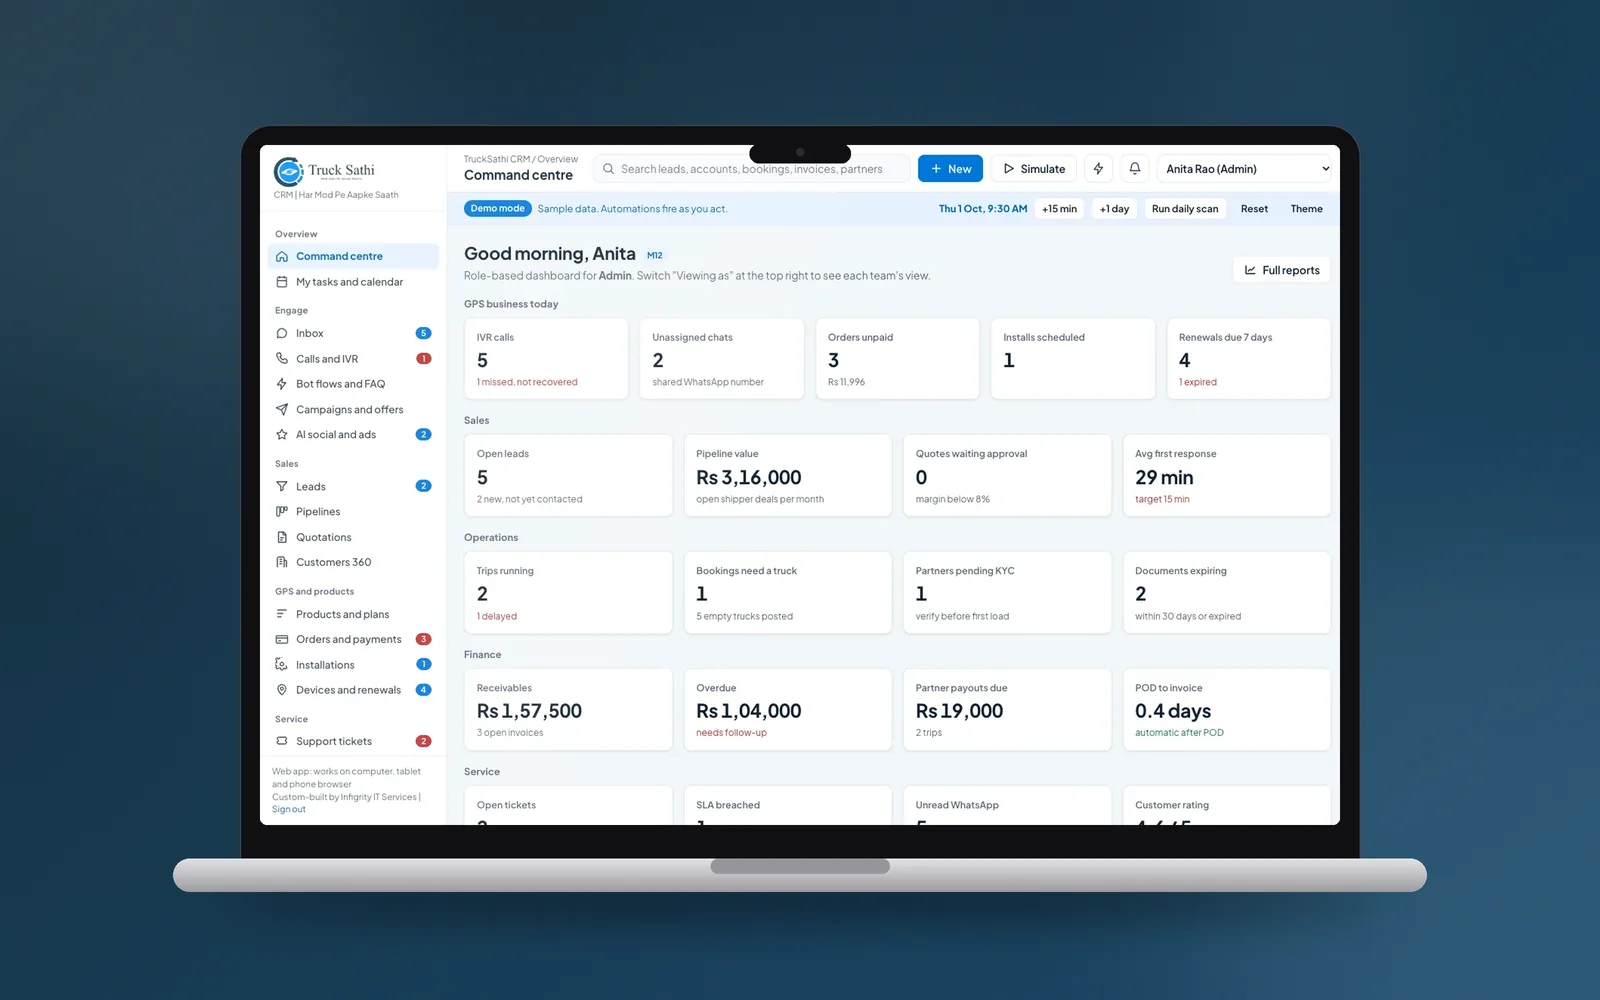
Truck Sathi CRM: live since November 2026
Fixed
scope, price and milestones before work starts
Yours
code, designs, data and accounts from day one
What is included?
- 01
Security Audits
Vulnerability assessments across web and mobile applications.
- 02
Penetration Testing
Controlled, authorized testing to find weaknesses before an attacker does.
- 03
Secure Architecture Review
Review of new and existing systems for access control and data handling gaps.
- 04
Incident Response Planning
Remediation guidance and a plan for when something does go wrong.
Why Infigrity for Cyber Security?
Security From Architecture, Not an Afterthought
Review happens at the design stage, not as a scramble the week before launch.
Production-Safe by Default
Penetration testing is scoped and scheduled around your traffic patterns, using production-safe methods unless you want a more aggressive test.
Fixes Ranked by Severity
You get a clear report with prioritized remediation steps - not just a list of vulnerabilities and no guidance on what to fix first.
Support for Compliance Requirements
We handle the technical controls behind common data-protection standards, working alongside your legal or compliance team.
Cyber Security work
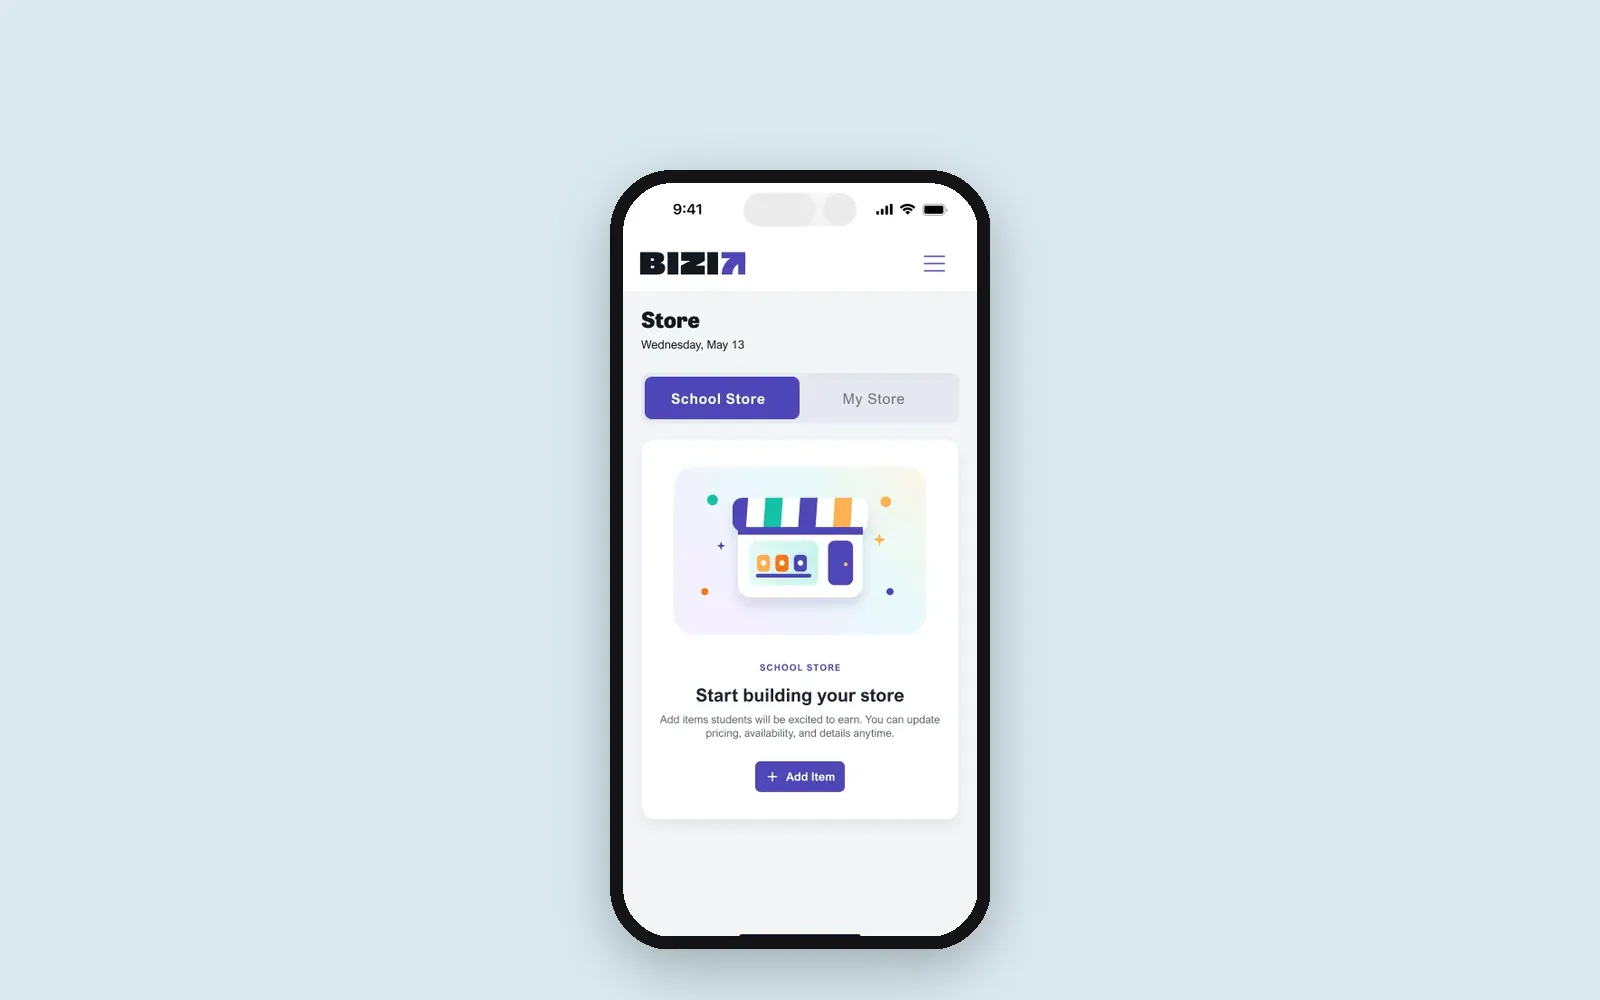 Live on App Store and Google Play
Education · United States
Bizi: a classroom rewards app for US schools, live on iOS and Android
- Flutter
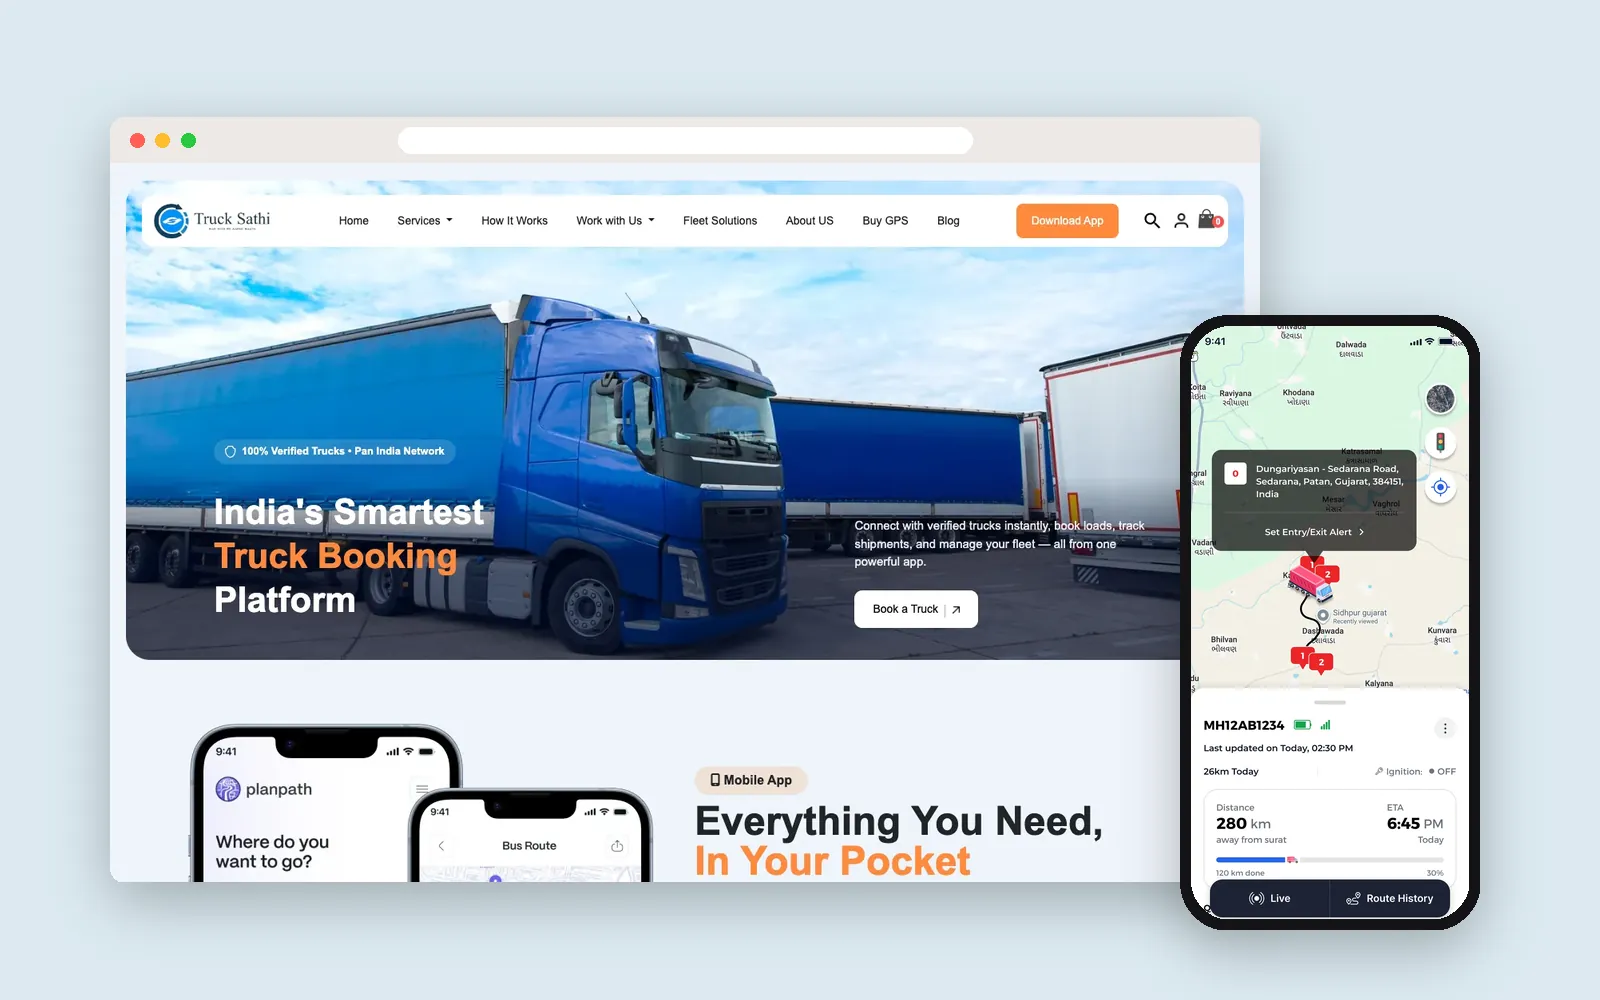 Live on Google Play
Logistics · India
Truck Sathi: truck booking, live GPS tracking and a custom CRM in 8 Indian languages
- Flutter
- WooCommerce
- WordPress
- Laravel
- Next.js
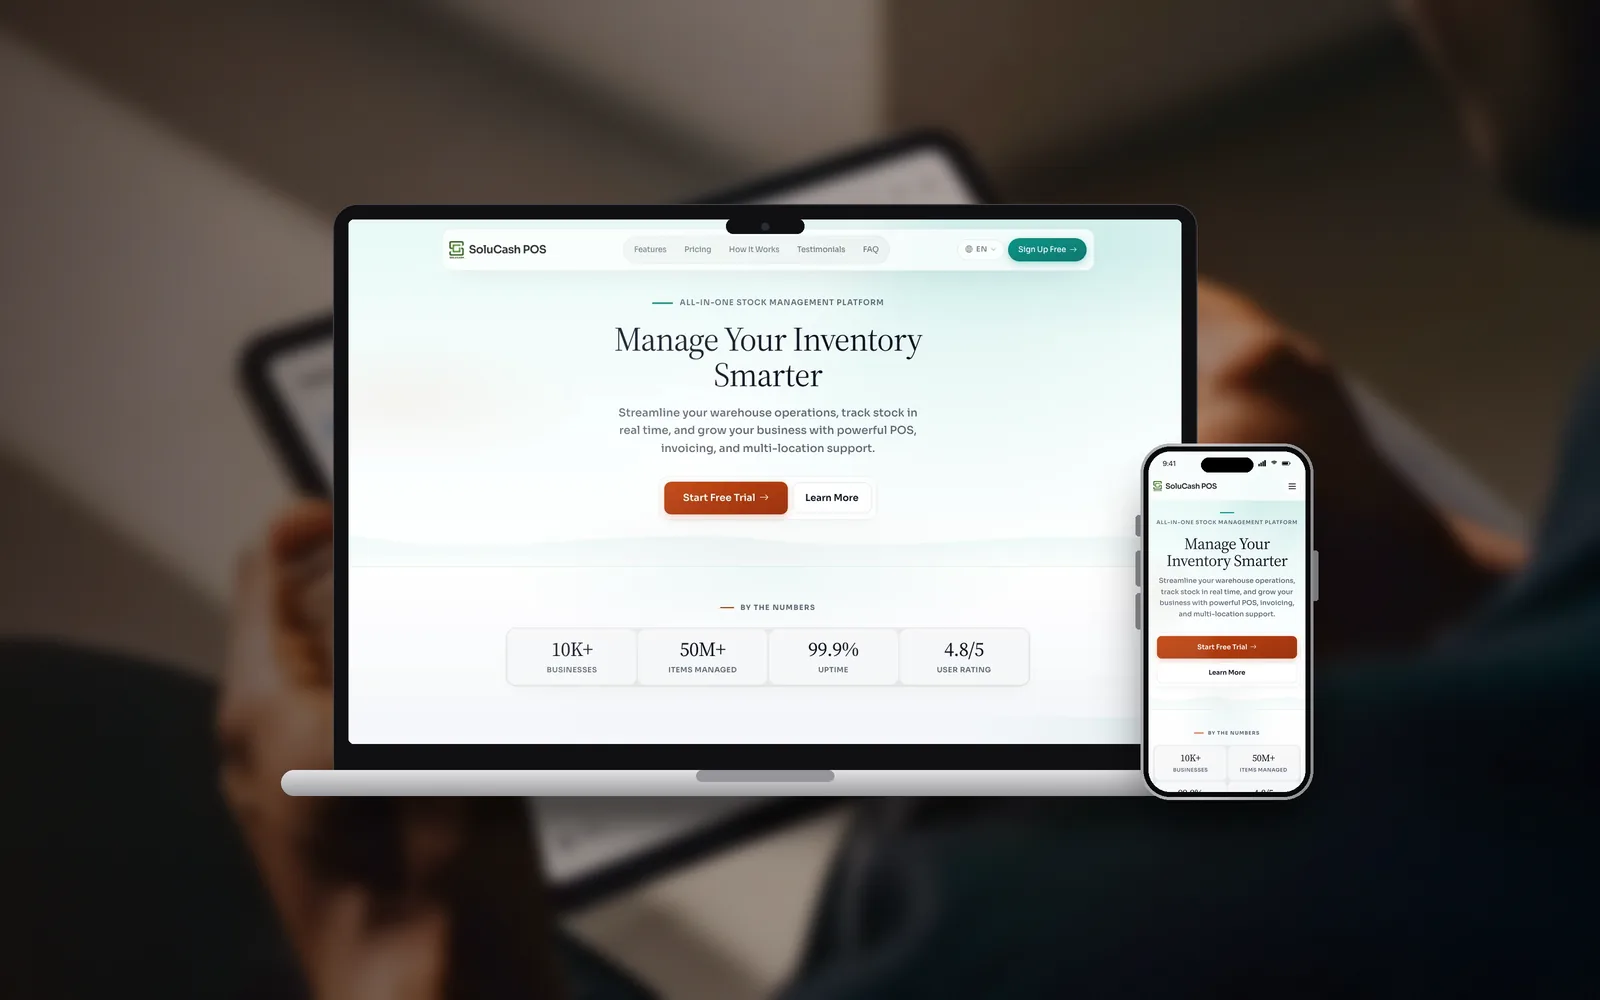
Technology & SaaS
SoluCash: a point-of-sale and business platform for companies across Africa
Not sure your last security review actually covered what matters? Let's find out.
Get a fixed quote and clear milestones after a free call.
How we deliver Cyber Security
- 1
Security Audit
A structured review of your current systems, access controls and data handling.
- 2
Vulnerability Assessment
Identifying specific weaknesses across your application and infrastructure.
- 3
Penetration Testing
Controlled, authorized testing to confirm which vulnerabilities are actually exploitable.
- 4
Remediation
Clear, prioritized fixes - not just a report - for the issues found.
- 5
Ongoing Monitoring
A monitoring plan so new vulnerabilities are caught as your system evolves.
Ways to work with us
Time & Material
For ongoing security monitoring as your systems keep evolving.
- Change scope as requirements evolve
- Pay based on work delivered
- Sprint-based delivery and review
- Full visibility into progress
Dedicated Team
Extend your team with security engineers who work inside your development process.
- Resourcing matched to your exact needs
- Direct daily collaboration with your team
- Scale the team up or down as needed
- Guaranteed committed hours
Fixed Price
For a clearly scoped audit or penetration test with a defined timeline.
- Scope agreed upfront
- Milestone-based delivery
- Fixed timeline and budget
- Best for well-defined projects
Frequently asked questions
Do you offer one-time audits or ongoing security monitoring?
Both - a one-time audit and penetration test suits a pre-launch check or compliance requirement; ongoing monitoring suits systems handling sensitive data continuously.
Will a security audit disrupt our production systems?
Penetration testing is scoped and scheduled around your traffic patterns, with production-safe testing methods used by default unless you specifically want a more aggressive test.
Can you help with compliance requirements?
Yes - we support the technical controls behind common data-protection requirements, though compliance certification itself typically involves your legal/compliance team alongside our technical work.
What do we get at the end of an engagement?
A clear report of findings ranked by severity, with specific remediation steps - not just a list of vulnerabilities without guidance on what to fix first.
More in SaaS and Custom Software
Often paired with
Ready to start your Cyber Security project?
Tell us what you need. We reply within one business day with next steps, a rough timeline and the questions that matter.